
Security your regulator can read.
Application security assessments, strong customer authentication and compliance readiness for banks, insurers, pharma and medtech. Findings reported in 10 working days, fixes delivered by the engineers who found them.
What we hear before a project starts.
“SMS codes no longer protect our customers.”
“DORA and the regulator want evidence, not intentions.”
“Our AI projects have no security owner.”
Assess, protect, comply.
Application security assessment
Web, mobile and API review (OWASP ASVS and MASVS), authentication and session design, code review of critical paths, cloud configuration. A report with severity, exploit scenario and fix per finding, re-test included.
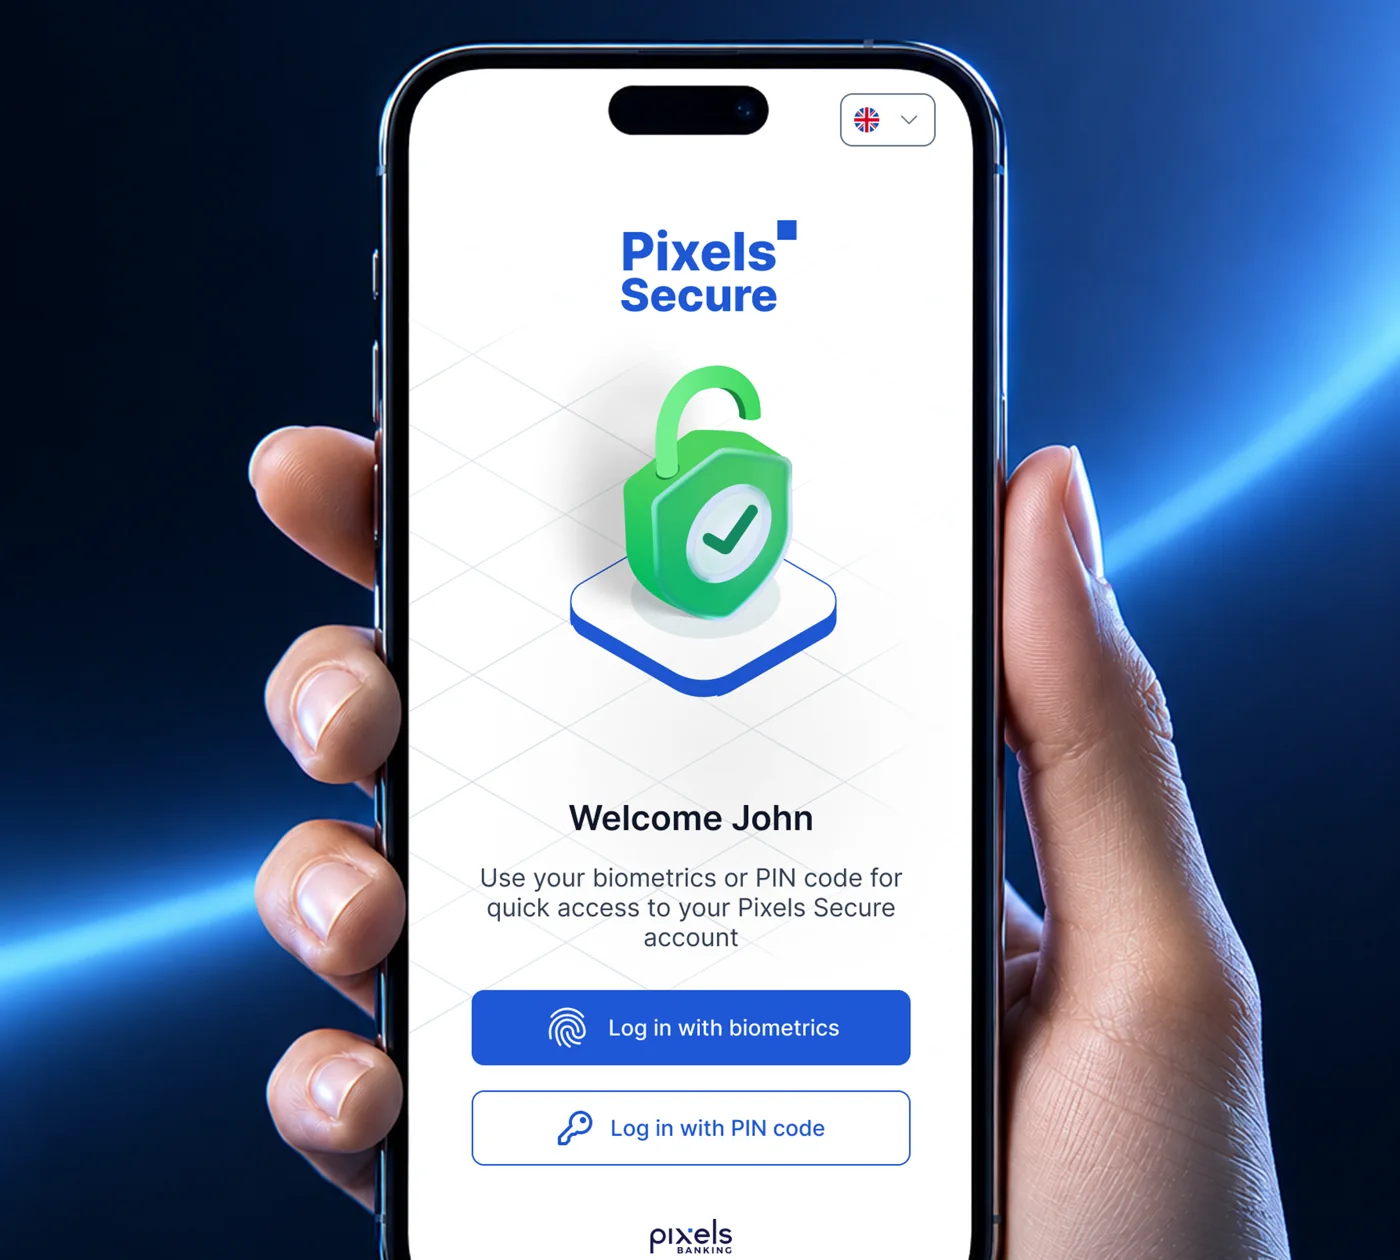
Strong authentication with Pixels Secure
Login and transaction approval in the customer’s app, biometric confirmation, device and SIM integrity checks, protection against SIM swap and eSIM fraud, integration with existing e-banking.
Proof. Pixels Banking.
Secure software development
Threat modelling, secure architecture, dependency and SBOM management, CI security gates, secrets management, logging and monitoring. Included in every platform or device project.
Compliance readiness
DORA (ICT risk, incident reporting, third-party register), Swiss nFADP and GDPR, FINMA circulars on operational risk, ISO 27001 preparation and the EU AI Act. Gap analysis, action plan, templates and support until the audit.
Email, domain & identity hardening
DMARC, SPF, DKIM, DNSSEC, MFA roll-out, anti-fraud procedures for finance teams and awareness sessions.
Proof. Our own domains run DMARC reject and DNSSEC, with a documented CEO fraud procedure.
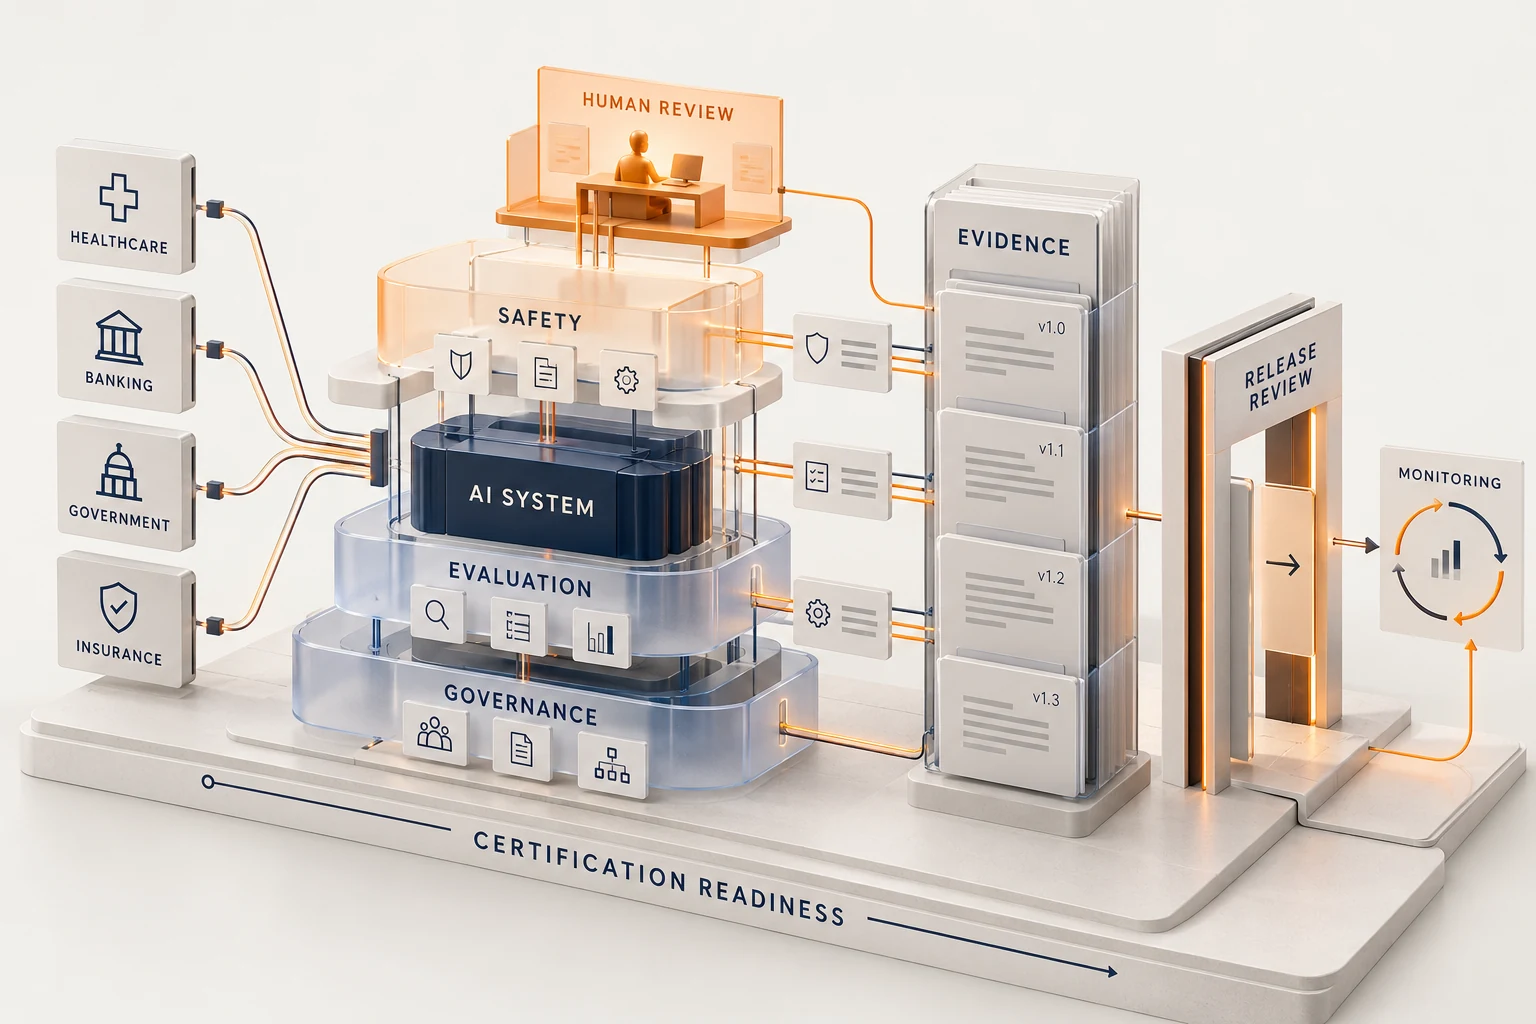
Extend security to the AI system
Retrieval, models and agents add new boundaries to assess. Combine access controls, adversarial evaluation and human governance with an evidence trail for the defined use.
Most security firms stop at the report.
We built the banking applications we now assess, so each finding comes with a fix we can implement, and each fix is tested against the real integration. One partner, from the finding to the patched release.
From scoping call to attestation.
Perimeter, access and objectives.
Manual testing of critical flows.
Findings and an executive readout.
Fixes delivered by the same engineers.
Optional continuous monitoring.
Banking security references


Three ways to start.
Fixed price, quoted after the free audit.
Mobile banking security assessment
3 weeks · Fixed priceAssessment of a mobile banking app and its APIs, with report and re-test.
DORA readiness
4 weeks · Fixed priceGap analysis, action plan and templates.
Pixels Secure integration
8 to 12 weeksLicence and integration with your e-banking.
Cybersecurity, answered
Is this a penetration test?
It is an application security assessment with manual testing of critical flows. For a full-scope red team we work with external penetration testing partners on request.
Do you need our source code?
It is recommended but not required.
Can you sign an NDA and work on site?
Yes, before the first call if you prefer.
Does Pixels Secure replace our e-banking?
No. It integrates with your existing e-banking.
Which standards do you follow?
OWASP ASVS and MASVS, NIST SP 800-63 AAL2 and AAL3, and ISO 27001 controls.
Let’s start with one hour.
In a free one-hour audit we map your three most valuable use cases, the constraints on your data and a realistic budget and timeline. No slides, one senior engineer.